.NET Apps Supported
While CloudEyE is designed for native applications, it can also protect certain .NET applications, depending on compatibility. However, already obfuscated .NET assemblies are not supported.
Fast on-the-fly updates
Many protection updates can be delivered server-side, reducing the need to update the client and helping keep protected applications current.
Compatible with most Windows versions
Protected and encrypted files are supported on Windows systems from Windows 7 / Server 2008 onward.
New protection concept
The encrypted file is stored on a remote server of your choice. The protected output securely downloads and decrypts it for in-memory execution.
Join needed files
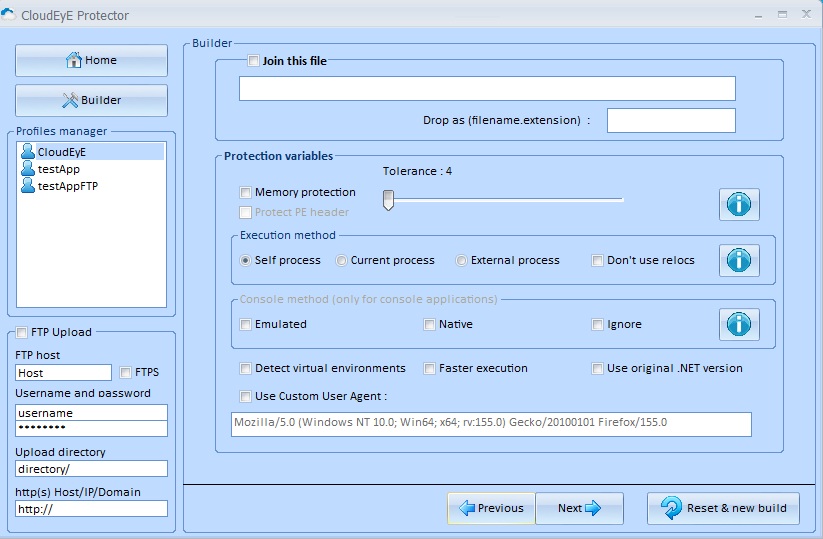
Bundle required companion files with the protected application, such as DLLs, configuration files or documentation.
Protect process memory
Help protect process memory against unauthorized dumping, scanning and modification to reduce exposure of sensitive application code and data.
Detailed FEATUREs
- Anti-debugging: Detects and prevents user-mode debugger activity.
- Anti-disassembly: Implements techniques designed to make static code analysis more difficult.
- Anti-API scanning: Helps prevent API-based analysis and inspection.
- Random code insertion: Inserts randomly generated garbage code between legitimate instructions.
- Polymorphic code: Protected routines use polymorphic code and instruction permutations to make pattern recognition more difficult.
- Anti-tracing: Uses a Vectored Exception Handler (VEH) to interfere with code-flow tracing and inspection.
- Unique code flow: Each protected application uses a different code-flow structure.
- Thread protection: Application threads are protected against unauthorized inspection and manipulation.
- Advanced entry-point protection: Protects the application's entry point against analysis and tampering.
- Advanced anti-breakpoint: Implements advanced techniques to prevent software breakpoints from being used to analyze the protected application.
- Debugger-hider resistance: Implements techniques designed to counter common debugger-hiding and anti-anti-debugging techniques.
- Memory scanner protection: Restricts access to individual memory pages and allows access only to pages that are actively required by the application.
- Memory patching protection: Implements mechanisms designed to prevent unauthorized modification of protected memory.
- Protected execution environment: The application executes within a protected runtime environment.
- No original code in the protected output: The protected application does not contain the original application's code in its original form.
- No disk extraction: The original application is never written to disk during protected execution.
Server-Side Application Protection & Access Control
By combining CloudEyE's application-level protection with server-side access controls, you can add a powerful layer of remote control and access management to your protected applications.
When the protected file is hosted on a server under your control, end-user can optionally provides an additional layer of server-side access control.
This enables features such as:
- Execution revocation: Remotely block content of the protected application without modifying or rebuilding the protected file.
- Geographic and network filtering based on country, IP address, VPN or Tor indicators. Server-side filtering solutions can be used to apply additional access rules.
- IP-based access control: Restrict application execution to trusted IP addresses only.
- Execution limits: Restrict the number of times the protected application can be executed using server-side controls.